These Fortinet FCSS_SASE_AD-25 sample questions are a small glimpse of our full set of Fortinet FCSS_SASE_AD-25 actual questions. They give you a preview of what the real FCSS_SASE_AD-25 exam might look like and the contents of Pass4Future's premium Fortinet FCSS_SASE_AD-25 product. You must not underestimate the value of Fortinet FCSS_SASE_AD-25 practice exam questions, as they allow you to understand the actual FCSS - FortiSASE 25 Administrator exam in greater depth. Using them will save your time and money otherwise wasted in FCSS - FortiSASE 25 Administrator exam reattempts. Study guides and tutorials provide you with theoretical details about the FCSS_SASE_AD-25 exam; these FCSS_SASE_AD-25 practice exam questions prepare you to pass the exam. Get Pass4Future's premium access to continue your FCSS_SASE_AD-25 exam practice with the complete set of Fortinet FCSS_SASE_AD-25 realistic questions. Our Fortinet FCSS_SASE_AD-25 practice questions come in various formats; make sure to check out the details and free demo of each format.
Do you know that you can access more real Fortinet FCSS_SASE_AD-25 exam questions via Premium Access? ()
Which FortiSASE feature ensures least-privileged user access to corporate applications that are protected by an on-premises FortiGate device?
Answer : B
ZTNA enforces least-privileged access by verifying user identity and device posture before granting access to specific corporate applications, even when protected by an on-premises FortiGate.
Which information does FortiSASE use to bring network lockdown into effect on an endpoint?
Answer : C
FortiSASE uses ZTNA tags to assess the endpoint's security posture. If the posture is non-compliant based on predefined rules, FortiSASE enforces network lockdown to restrict access accordingly.
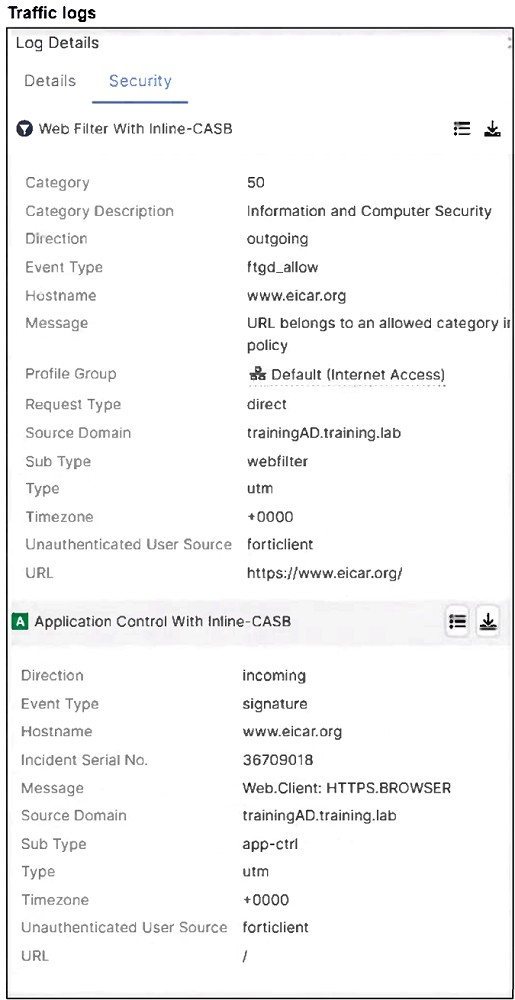
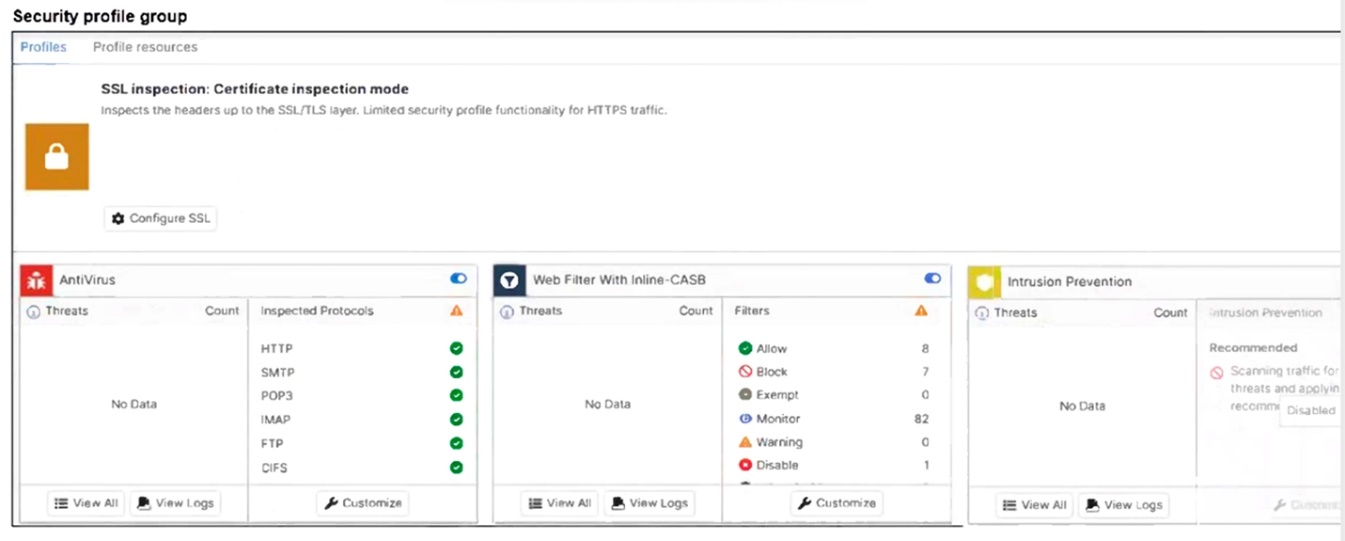
Refer to the exhibits.


A FortiSASE administrator has configured an antivirus profile in the security profile group and applied it to the internet access policy. Remote users are still able to download the eicar.com-zip file from https://eicar.org.
Which configuration on FortiSASE is allowing users to perform the download?
Answer : B
The SSL inspection mode is set to certificate inspection, which only inspects SSL/TLS headers and does not allow full scanning of encrypted content. Without full (deep) inspection, the antivirus profile cannot scan or block malicious files (like eicar.com-zip) delivered over HTTPS, allowing the download to proceed.
Which authentication method overrides any other previously configured user authentication on FortiSASE?
Answer : D
Single Sign-On (SSO) overrides any other previously configured user authentication method on FortiSASE, taking precedence for user authentication.
Your FortiSASE customer has a small branch office in which ten users will be using their personal laptops and mobile devices to access the internet.
Which deployment should they use to secure their internet access with minimal configuration?
Answer : B
Deploying FortiAP enables secure internet access for unmanaged personal devices in small branch offices with minimal configuration by automatically directing traffic through FortiSASE, eliminating the need for endpoint installation or complex setup.