Pass4Future also provide interactive practice exam software for preparing Microsoft Administering Windows Server (AZ-802) Exam effectively. You are welcome to explore sample free Microsoft AZ-802 Exam questions below and also try Microsoft AZ-802 Exam practice test software.
Do you know that you can access more real Microsoft AZ-802 exam questions via Premium Access? ()
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with a Microsoft Entra tenant. You deploy an app that adds custom attributes to the domain. From Azure Cloud Shell, you discover that you cannot query the custom attributes of users. You need to ensure that the custom attributes are available in Microsoft Entra ID. Which task should you perform from Microsoft Entra Connect first?
Answer : A
When an application extends the on-premises AD DS schema by adding new custom attributes after Microsoft Entra Connect has already been installed and configured, the sync engine's local, cached copy of the AD schema (used to populate the attribute-selection lists for sync rules and attribute mappings) does not automatically become aware of the newly added attributes. Microsoft Entra Connect provides a 'Refresh directory schema' task, run from the Microsoft Entra Connect wizard, specifically to re-read the current AD DS schema and update the sync engine's local metadata so that the newly introduced custom attributes become visible and selectable for synchronization rules and attribute-flow configuration. Only after this refresh has completed can an administrator configure a rule (via directory extension attribute sync, or a custom sync rule) that actually flows the new attributes to Microsoft Entra ID, at which point they would finally be queryable from Azure Cloud Shell (for example, via Microsoft Graph). 'Configure device options' pertains to device registration/writeback settings, not attribute sync. 'Customize synchronization options' is used to reconfigure existing sync features (such as enabling or changing which optional features are active) and, without a preceding schema refresh, still would not expose attributes the sync engine's cached schema doesn't yet know about. 'Manage federation' configures AD FS/federation trust settings and is unrelated to attribute synchronization. Therefore, the first task to perform is to refresh the directory schema.
You have 10 servers that run Windows Server in a workgroup. You need to configure the servers to encrypt all the network traffic between the servers. The solution must be as secure as possible. Which authentication method should you configure in a connection security rule?
Answer : D
Because the ten servers are in a workgroup rather than joined to an Active Directory domain, Kerberos V5 is not usable as an authentication method for a connection security rule, since Kerberos V5 depends on a domain controller acting as the Key Distribution Center, which workgroup servers do not have access to. Of the remaining options actually usable in a workgroup, a computer certificate issued from a trusted certification authority provides much stronger, mutually verifiable authentication than either a shared pre-shared key or NTLMv2. Windows Defender Firewall with Advanced Security guidance explicitly identifies pre-shared keys and NTLM-based authentication as weaker fallback methods appropriate only when certificates or Kerberos are unavailable, precisely because a pre-shared key is a single shared secret with no per-computer identity verification and NTLMv2 is an older, less robust protocol vulnerable to several known attack classes. Certificate-based authentication, by contrast, lets each server present its own distinct, verifiable identity, making it the most secure choice available for encrypting workgroup server-to-server traffic. Therefore, computer certificate authentication is the correct choice.
You have two servers named Server1 and Server2 that run Windows Server. Both servers have the Hyper-V server role installed. Server1 hosts three virtual machines named VM1, VM2, and VM3. The virtual machines replicate to Server2. Server1 experiences a hardware failure. You need to bring VM1, VM2, and VM3 back online as soon as possible. From the Hyper-V Manager console on Server2, what should you run for each virtual machine?
Answer : C
A Planned Failover in Hyper-V Replica requires the source (primary) virtual machine to be gracefully shut down and reachable so that any final, not-yet-replicated changes can be sent across before the role formally switches to the replica -- a precondition that cannot be met when the primary host itself has suffered a hardware failure and is unreachable. Because Server1 has failed and VM1, VM2, and VM3 cannot be contacted, gracefully shutting them down is impossible, ruling out Planned Failover as an option. Instead, the administrator must perform an Unplanned Failover from Hyper-V Manager on Server2, which brings each replica virtual machine online using whatever data was most recently replicated (and, if recovery points are configured, the most recent available recovery point) without requiring any action on, or connectivity to, the failed primary host. This is the recovery path specifically documented for unexpected primary-host outages, in direct contrast to Planned Failover, which is reserved for scheduled maintenance or controlled, orderly migrations where the primary is still running. 'Start' merely powers on an existing VM without invoking replica failover logic, and 'Move' performs a live or quick migration that requires the source host to be online, so neither applies here. Therefore, Unplanned Failover is the correct action for each virtual machine.
You have a Hyper-V host named Server1 that runs Windows Server. Server1 hosts a virtual machine named VM1 that runs Windows Server and has multiple file shares. You have an Azure subscription. You need to migrate the file shares to Azure Storage by using Azure Storage Mover. The solution must minimize downtime and administrative effort. What should you do on the on-premises network first?
Answer : A
Azure Storage Mover uses a purpose-built migration agent that is deployed as its own dedicated virtual machine on the on-premises hypervisor rather than as software layered onto an existing guest operating system, so for a Hyper-V environment the correct first step is to download the agent's VHD image from the Storage Mover resource in Azure and use it to create a new, separate agent virtual machine on the Hyper-V host, Server1, that hosts the source VM whose file shares need migrating. Once that agent VM is powered on and registered against the Storage Mover resource using an activation key generated in the portal, it can enumerate and transfer the file shares hosted on VM1 with minimal ongoing administration, running the actual copy jobs in the background while VM1 continues serving those shares, and without installing any agent software inside VM1 itself. This approach differs from Azure Migrate's Connected Machine agent, which is used for a different assessment-and-lift-and-shift migration workflow that projects on-premises machines into Azure as Azure Arc resources rather than for file-share transfer through Storage Mover, and installing it on either VM1 or Server1 would not accomplish the file-share migration the scenario requires.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. You are planning the deployment of DNS to a new network. You have three internal DNS servers as shown in the following exhibit (Server1/Montreal/10.0.1.10/contoso.local, Server2/Toronto/10.0.2.10/east.contoso.local, Server3/Seattle/10.0.3.10/west.contoso.local). The contoso.local zone contains zone delegations for east.contoso.local and west.contoso.local. All the DNS servers use root hints. You need to ensure that all the DNS servers can resolve the names of all the internal namespaces and internet hosts. Solution: On Server2 and Server3, you configure a conditional forwarder for contoso.local. Does this meet the goal?
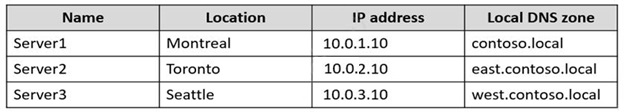
Server1 (Montreal, 10.0.1.10, contoso.local) / Server2 (Toronto, 10.0.2.10, east.contoso.local) / Server3 (Seattle, 10.0.3.10, west.contoso.local); contoso.local delegates east.contoso.local and west.contoso.local.
Answer : A
Windows DNS Server evaluates conditional forwarders using longest-suffix matching, so a conditional forwarder configured for the domain contoso.local also catches queries for names under that suffix, including the delegated child namespaces east.contoso.local and west.contoso.local, when no more specific conditional forwarder exists for those subdomains. Pointing that conditional forwarder at Server1 (10.0.1.10) lets Server2 and Server3 hand off any query for the contoso.local namespace --- their own local zone's parent, the sibling zone, and the delegated zones alike --- to a server that is authoritative for contoso.local and holds the NS delegation records needed to chase down answers in east.contoso.local and west.contoso.local. Internet name resolution is unaffected by this change: the scenario states that all the DNS servers already use root hints, and a conditional forwarder scoped to contoso.local has no effect on queries for names outside that suffix, so Server2 and Server3 continue to resolve internet hosts directly through their existing root hints exactly as before. Because the combination of the pre-existing root hints (internet hosts) and the new conditional forwarder (the full internal contoso.local namespace, including both delegated child zones) covers every namespace the requirement asks for, this solution meets the stated goal.